




Cybersecurity your employees will actually use.
Short videos, plain language and 41 practical situations from real working life.
A changed supplier bank account, a domain that reads almost the same, a call from “the director”, a sign-in prompt you did not request. The company sees who has completed the course and with what result.
An independent educational product of the responsiblo platform. Not a programme of the European Union or of any national cybersecurity authority.
Your company account shows you
SAMPLE83%
20 of 24 completed
Emily Clarke
100%
James Walker
100%
Sophie Turner
63%
Daniel Hughes
25%
Updated today 9:14
Export overview →Does NIS2 apply to your organisation?
Answer up to three short questions and see an indicative result straight away. Your answers are not sent or stored.
You usually fall under NIS2 if:
- you work in a sector named in the directive, such as energy, water, banking, healthcare, air, rail or water transport, cloud and managed IT services, selected manufacturing, the food industry, chemicals, waste, postal services or research,
- and you employ at least 50 people, or your annual turnover and total assets both exceed EUR 10 million,
- or you provide public electronic communications networks or services, DNS services or electronic signature services; for these, size does not matter.
- Central government bodies are covered regardless of size; for regions, municipalities and schools, national law decides.
This is only an indicative estimate based on the NIS2 Directive, not legal advice. Whether and how the rules apply to you is set by national law, which differs in details from country to country; your national cybersecurity authority provides guidance.
Question 1 of 3
What does your organisation do?
What counts is what you provide to others, not what you use yourselves. If more than one fits, choose the highest one.
- Telecoms, DNS, electronic signatures
- Public electronic communications networks and services, DNS services, top-level domain registries, registering domain names for others (including reselling), electronic signatures, seals and time stamps. Only using a domain, phone or e-signature does not count.
- Energy, water, healthcare, banking
- Producing and supplying electricity, gas, heat, oil and hydrogen, charging points (not installation or servicing); drinking and waste water; banks, stock exchanges, central counterparties; healthcare including medical labs, medicine research and production. Not insurance, leasing, lending or accounting.
- Air, rail and water transport, cloud, IT management
- Airports, airlines, rail and shipping companies, ports, road traffic management; cloud, data centres, internet exchange points; managing IT or security for other companies; space services. Not road haulage, bus or taxi services, freight forwarding, software development or web design.
- Selected manufacturing, food, chemicals, waste, postal, research
- Making electronics, electrical equipment, machinery, vehicles and medical devices (activities in NACE divisions 26 to 30); industrial food production and wholesale; chemicals; waste; post and couriers; online marketplaces for other traders, search engines, social networks; commercial research. Not food shops, restaurants or your own online shop. Other manufacturing usually does not count; if you process chemical substances or mixtures, check with your national authority.
- Public authority, region, municipality, school or university
- Ministries and central government bodies, regions, municipalities, schools and universities. The directive excludes courts, parliaments and central banks.
- None of these
- For example insurance, road transport, software development, retail, restaurants, construction and most services.
Question 2 of 3
How many people does your organisation employ?
Count full-time equivalents for the last completed financial year, including owners who work in the business, but not apprentices or students in vocational training. If you belong to a group of companies, add those that control you or that you control.
Question 3 of 3
Do both your annual turnover and your total assets (balance sheet total) exceed EUR 10 million?
You will find turnover (excluding VAT) and total assets in your latest approved annual accounts. It is enough that one of the two figures is EUR 10 million or less. In a group of companies, include those that control you or that you control.
Probably yes, in the stricter regime (essential entity)
Under the directive, large organisations in key sectors fall under the stricter regime. They must take cybersecurity risk-management measures, and the directive explicitly names training among them. Management must complete training, and staff should be trained regularly.
Probably yes, likely in the less strict regime (important entity)
Your organisation probably falls under the less strict regime, or the stricter one if turnover exceeds EUR 50 million and assets EUR 43 million. Either way, it must take cybersecurity risk-management measures, including training: management must complete it, and staff should be trained regularly.
Probably yes, in the less strict regime (important entity)
Under the directive, organisations in these sectors fall under the less strict regime; a country can exceptionally apply the stricter one. Even so, they must take cybersecurity risk-management measures, including training: management must complete it, and staff should be trained regularly.
Probably yes, whatever the size of your organisation
The directive covers the services you selected regardless of size. The regime depends on the service. For domain registration alone, the duties mainly concern registrant data. For the other services, the measures include training: management must complete it, and staff should be trained regularly.
Probably not directly, but it may reach you through your customers
You probably do not fall under the directive yourselves. Customers who do, however, must address the security of their direct suppliers and may ask you for it in the contract, including training for your people.
NIS2 probably does not apply to you
Based on your answers, the directive probably does not apply to you directly. However, national law may cover further sectors, and a country can exceptionally designate a specific organisation. If you supply organisations covered by NIS2, they may ask you for security and staff training.
We can't tell from these answers
Without your sector we cannot give a reliable estimate. What matters is your main activity, meaning what you provide to others. Go through the options again or ask us. Until then, assume that NIS2 may apply to you.
We can't tell from these answers
Without your organisation's size we cannot give a reliable estimate. You will find headcount, turnover and assets in your annual accounts, or ask your accountant or HR. Until then, assume that NIS2 may apply to you.
Central government yes, others depend on national law
The directive covers central government bodies regardless of size. It covers regional bodies if the country selects them after a risk assessment, and municipalities and schools only if national law includes them. Check with your national cybersecurity authority.
This is only an indicative estimate based on the NIS2 Directive, not legal advice. Whether and how the rules apply to you is set by national law, which differs in details from country to country; your national cybersecurity authority provides guidance.
Why now
Attacks target people, not servers
Many incidents start with a message, a call or a request that looks normal. Technology helps, but the decisive moment is a person who stops and verifies. The NIS2 Directive therefore counts employee training among the risk-management measures.
NIS2 in brief
The NIS2 Directive lists basic cyber hygiene practices and cybersecurity training among risk-management measures and expects management bodies to be trained as well.
Articles 20 and 21(2)(g) of Directive (EU) 2022/2555 (text on EUR-Lex).
What the course does
It teaches people to recognise a situation in which it is better to stop, verify or report, and gives the company an overview of who has been trained.
17 Oct 2024
Deadline for national NIS2 laws
75 to 90 min
The whole course including practice and the final check
41
Practical real-life situations in 8 chapters
The course practises situations every company knows
How the course works
75 to 90 minutes in total
Invitation
Employees get an invitation or an access code from their company.
8 chapters
A short video and text for every chapter.
Practice
41 real-life situations; mistakes are allowed.
Final check
12 questions at the end, pass mark 75%.
Overview
The company sees who has completed the course.
Course content
Eight chapters that matter to everyone at work
Attacks target people
Six pressure levers and two questions before every step.
Phishing: messages, links and attachments
A domain that reads almost the same; where a link really goes; an attachment that asks for more.
Calls, texts and voices that are not real
A text from “the bank”, a call from “the director”, a QR code instead of a link.
Passwords and sign-in
Length, uniqueness, a password manager and prompts you did not start.
Devices, updates and unknown files
Updates on time, never an unknown drive, a clean desk.
Company data and sharing
The right recipient, the necessary scope, an approved tool, including AI.
Working outside the office
Wi-Fi, the home office, a stranger at the door, a lost laptop.
When something happens
Report the facts in time, do not make it worse, access rights when a colleague leaves.
Final check
12 questions, pass mark 75%. After a successful check the participant gets a personal certificate and the result goes into the company's overview.
Course for management
The eight chapters of the employees' course and three chapters for management: what NIS2 expects from management; incidents, deadlines and suppliers; training, records and what not to claim. A final check of 18 questions and its own certificate.
I want the management coursePractice
Try it right now
Short practical situations belong to the chapters. The brands and institutions in the exercises are real, because they are the ones fraudsters pretend to be. Addresses, numbers and messages are fictional. Try one exercise from every lesson right here. Your choices are sent only to be evaluated and are not stored.
- Chapter 1 Attacks target people Sample: Five seconds: safe or risky? · Quick series In the course: What would work on you? · Matching
- Chapter 2 Phishing: messages, links and attachments Sample: Two domains, five seconds · Spotting the difference against the clock In the course: Morning inbox · Sorting inbox In the course: Where does that link go? · Where a link really leads In the course: Mark what warns you · Marking the warning signs In the course: The spreadsheet wants macros · Situation with three options In the course: An invoice with a new account · Comparing documents In the course: The supplier writes a third time · Branching story
- Chapter 3 Calls, texts and voices that are not real Sample: The director calls from a conference · Branching story In the course: A text from the bank · Simulated conversation In the course: Is it really them? · Situation with three options In the course: A QR code on a poster and in an email · Finding the risks in a scene In the course: A colleague needs your access · Simulated conversation In the course: Quick series: phone in hand · Quick series
- Chapter 4 Passwords and sign-in Sample: The phone wants you to approve a sign-in · Phone with prompts In the course: Password lab · Password lab In the course: A password leaked from an online shop · Branching story In the course: Which sign-in page is genuine? · Spotting the difference against the clock In the course: Password manager, passkey, code: what is what · Matching
- Chapter 5 Devices, updates and unknown files Sample: Find the risks on the desk · Finding the risks in a scene In the course: Update or meeting · Situation with three options In the course: A USB stick outside the meeting room · Situation with three options In the course: Which window is real? · Marking the warning signs In the course: I need to convert a PDF · Branching story
- Chapter 6 Company data and sharing Sample: What may go into an AI tool · Sorting into bins In the course: Sort the data · Sorting into bins In the course: A link for anyone · Situation with three options In the course: The attachment went to the other Sarah · Putting the steps in order In the course: What in the spreadsheet is personal data · Marking the warning signs
- Chapter 7 Working outside the office Sample: A stranger at the door · Simulated conversation In the course: The hotel Wi-Fi wants a certificate · Branching story In the course: Finishing work on the family laptop · Situation with three options In the course: The laptop stayed on the train · Putting the steps in order In the course: Home office · Finding the risks in a scene In the course: Quick series: your phone at work · Quick series
- Chapter 8 When something happens Sample: Put together a report · Putting together a report In the course: You have already entered your password · Branching story In the course: Files will not open: what now · Branching story In the course: A former colleague can still see the folder · Situation with three options In the course: Report it or not? · Quick series
- Lesson 9 What NIS2 expects from management Sample: Management duties: what goes with what · Matching In the course: What "compliance" is and is not · Quick series
- Lesson 10 Incidents, deadlines and suppliers Sample: Reporting deadlines: 24 hours, 72 hours, final report · Timeline In the course: A supplier you give access to · Sorting into bins
- Lesson 11 Training, records and what not to claim Sample: Weekend incident · Branching story In the course: Training as a measure: what to record · Putting together a report
Mistakes are allowed: you see at once what was risky and why. Only you see your points; the company sees completed chapters and the result of the final check.
The course is currently available in Czech.
Tell us what your team needs and we will get back to you.
Contact usChecklist: 12 steps to prepare your employees for NIS2
A practical PDF checklist for company management and the person responsible for cybersecurity. It walks you through management, employee training, incident reporting and suppliers, and shows how to document your preparation.
management takes the training first and approves the training plan
who is responsible for cybersecurity
who to train and how to handle induction training
regular training with practice and a check
one way to report and a plan for an incident
suppliers with access and records of training
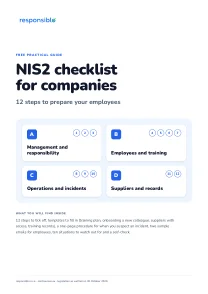
10 A4 pages, PDF
A resource from the NIS2 courses programme by responsiblo. English, version November 2026.
Free download
Get the Checklist FREE
Company account
Does your whole team need training?
Get in touch and we will reply within two working days. We will help you choose a package and the management course. For larger companies we also build an academy of their own with the company's logo and colours.
Invitations, the team overview and exports come with every package; they differ only in the number of people and the price
The company sees completed chapters and the result of the final check, not individual answers in the practice
Anyone can verify each employee's certificate by its number
Frequently asked questions
What people ask most often
Is the course free for individuals?
No. The course is designed for companies and organisations; the smallest package, Micro, covers 5 people. You can try a sample situation for free right here on this page.
Is this an official course of the EU or of an authority?
No. The course is provided by responsiblo as an independent educational platform. The personal certificate documents completion of the course and its final check, not certification of an organisation or legal compliance.
Is the course enough for NIS2?
Not on its own. Employee training is one measure alongside technical and organisational steps. What applies to your organisation is for the organisation or its advisers to assess. The text of Directive (EU) 2022/2555 is available on EUR-Lex.
What is the practice part?
41 real-life situations in 16 formats: sorting an inbox, spotting a domain difference against the clock, revealing where a link really goes, deciding in a branching story, sorting data by drag and drop. Mistakes are allowed; you see at once what was risky and why. It is not a graded test.
How long are the videos?
Short: no more than 2 minutes per chapter. Everything essential is also in the text below the video.
Is the course also for management and IT?
For management there is a separate course, Cybersecurity for Management: the eight chapters of the employees' course and three chapters on the role of management under NIS2, reporting deadlines and suppliers, with its own final check and certificate. IT administrators and security roles need further specialist training, which this course does not replace.
How often should training be repeated?
Your organisation sets the interval according to its rules and risks. The personal certificate is valid for 12 months; the course can be taken again afterwards.
In which languages is the course available?
The course is available in Czech.
Is your question missing? Ask us and you will have the answer within two working days. Ask a question
Start with cybersecurity today
Tell us how many people you want to train and we will get back to you within two working days.
Cybersecurity for Employees is an independent educational product of responsiblo s.r.o. It is not a programme of the European Union or of any national cybersecurity authority, nor is it endorsed by them. The content is not legal advice.